Cyberattack Hits Hundreds of French Supermarkets, Overheating Fridges and Sparking Fires. Could The Next Cyberattack Disrupt An Entire Supply Chain, From Phones To Traffic Lights And Hospital Equipment?
Hackers have found a way to turn supermarket refrigerators into ovens, ruining food and sparking fires across France. But what if the next target isn't a fridge? What if it's the phone in your hand, the traffic light at your next intersection or the equipment keeping a hospital patient alive?

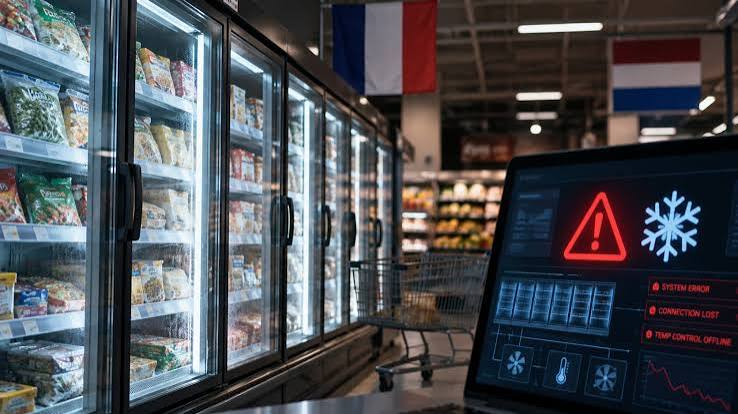
Hundreds of supermarkets across France have been hit by a cyberattack that did something few people would associate with hacking. Instead of stealing customer data or locking companies out of their computer systems, the attackers targeted refrigerators and freezers, pushing temperatures as high as 122°F (50°C), spoiling food and triggering fires at several stores.
The attack affected several major retail chains, including Intermarché, Carrefour, Monoprix and Coopérative U. Intermarché and its Netto brand reported that around 150 stores were affected, while Carrefour reported disruptions at 80 outlets. Coopérative U also reported widespread damage. With refrigeration systems compromised, stores were forced to discard fresh and frozen food to prevent potentially unsafe products from reaching customers.
The financial damage could be substantial. Intermarché chief executive Thierry Cotillard estimated that losses across the French retail sector could run into tens of millions of euros in a single day. The incident has also raised concerns about food security, given how much modern food retailing depends on refrigeration systems working continuously and reliably.
So how did hackers manage to interfere with something as ordinary as a supermarket refrigerator?
Large stores typically use centralised control panels to manage refrigeration across multiple display units. These systems allow operators and maintenance teams to monitor temperatures, manage defrosting cycles and identify faults without having to inspect every unit individually. That convenience, however, also means that the equipment relies on software and connected control systems.
French authorities identified a vulnerability involving refrigeration-management software supplied by Danish company Danfoss. The company said the affected systems were running outdated firmware and reiterated that customers should update supported equipment and migrate older systems where necessary.
The incident is now being investigated by French authorities, with the country’s National Cybersecurity Agency involved. But beyond the immediate damage, the attack raises a question that extends well beyond supermarket aisles.
The damage is visible, but who was behind it and what they intended to achieve – remains unknown.
But the more disturbing question is this – if hackers can interfere with the systems that keep food cold, what else could they disrupt by targeting the technology that quietly keeps everyday life running?
What Would Hackers Gain From An Attack Like This?
At first glance, attacking supermarket refrigerators seems like an oddly specific way to cause trouble. There are no obvious customer databases to steal, no bank accounts to empty and no ransom demand established in the reporting so far. Yet the consequences are tangible: spoiled food, damaged equipment, financial losses and disruption across hundreds of stores.
So what could the attackers possibly gain?
One possibility is financial. Cybercriminals frequently target businesses because the cost of disruption can make victims more willing to pay to restore normal operations.
An attack that damages inventory or threatens continued business could create pressure to negotiate. But without evidence of a ransom demand, financial extortion remains only one possible explanation for the French incident.
Another possibility is sabotage. Disrupting refrigeration systems can inflict economic damage without directly attacking a company’s finances. A retailer could lose millions in stock, face temporary closures and struggle to replenish its shelves. If the objective were to cause disruption rather than steal money, the damage itself could be the intended outcome.
There is also the possibility of a politically motivated attack. Disrupting food supplies, even temporarily, could generate public anxiety and raise questions about whether businesses and governments can protect essential services. In a more strategic scenario, an attacker might want to demonstrate that ordinary infrastructure can be interfered with through digital means.
But there is another possibility worth considering.
What if the objective was not just to damage the supermarkets, but to find out how much damage could be done in the first place?
An attack could potentially reveal how easily connected equipment can be accessed, how quickly a business detects a problem and how much disruption follows when a system stops functioning as intended. Those lessons could be useful to someone interested in exploiting similar weaknesses elsewhere.
This does not establish that the French attack was a test, nor does it tell us who was behind it. But it opens up a bigger question: if an attacker can manipulate one type of connected equipment, could the same broad approach be considered for other systems that businesses and the public depend on?
That is where the story becomes much bigger than refrigerators.
Could This Have Been A Test Run For Something Bigger?
What if the most important outcome of the French supermarket attack was not the food that had to be thrown away or the money retailers lost, but what the attackers might have learned from the disruption?
It is a question worth asking. In cybersecurity, an attack can serve more than one purpose. Apart from causing immediate damage, it could reveal weaknesses in connected equipment, expose gaps in an organisation’s response or demonstrate how much disruption a particular vulnerability can cause.
Imagine someone discovering that a particular type of refrigeration controller can be interfered with remotely. The first question might be whether the system can be accessed. The next might be what happens when it is disrupted. How quickly would the supermarket notice? Would its staff be able to override the system? Would backup arrangements prevent food from spoiling? And how long would it take to restore normal operations?
Now imagine those questions being asked about other types of equipment.
Could the same broad thinking be applied to the systems managing warehouse temperatures, coordinating deliveries or monitoring industrial machinery? Could someone examine how dependent businesses are on a particular manufacturer or software provider, and whether the same weakness exists across multiple locations?
This is the test-run possibility.
An operation that appears limited in scope could, in theory, help someone understand the practical consequences of interfering with connected infrastructure before considering a more ambitious target.
The potential implications become more serious if the objective is strategic rather than financial. A criminal group might be interested in finding another way to extort money. A politically motivated group might want to demonstrate its reach. A state-linked actor, in a hypothetical scenario, might be interested in understanding vulnerabilities that could matter during a future conflict.
There is no established evidence that the French attack was designed as a rehearsal for a larger operation. But the question it raises is difficult to ignore: if connected equipment can be disrupted in one setting, what other systems might someone consider targeting?
From Refrigerators To Phones, Telecom Networks And Satellites
Most people think about cyberattacks in terms of stolen passwords, hacked social media accounts, leaked personal information or money disappearing from a bank account. But what if the target were not the information on a device, but the service that device depends on?
Consider the mobile phone. A compromised phone can expose its owner’s information or communications. Disrupting the network connecting millions of phones is a different proposition altogether. If a mobile operator experienced a major outage following a cyberattack, people could lose access to calls, messages and mobile internet. Businesses might struggle to coordinate deliveries, digital services could become inaccessible and people might have difficulty reaching emergency services through their usual channels.
The same question applies to internet service providers. A widespread disruption could affect offices, payment systems, online services and households simultaneously. The impact would depend on the scale of the outage, the networks involved and the availability of alternative connections.
Then there are satellites.
Satellite television might appear to be a relatively harmless example, but satellite infrastructure is used for much more than broadcasting entertainment. Depending on the system, satellites support communications, navigation, weather forecasting and other services. An attack that interrupts a television broadcast would have a very different impact from one that disrupts a satellite communications network used by businesses or public services.
The 2022 cyberattack on Viasat’s KA-SAT network offers a real-world illustration. The attack disrupted satellite internet connectivity for tens of thousands of users across Europe, including communications associated with wind turbines. The incident demonstrated how a cyberattack on a communications network could affect services far beyond the immediate target.
Now return to the question raised by the French supermarkets. If the systems controlling refrigeration can become a point of disruption, what happens when the target is a network connecting millions of people or businesses?
What If Traffic Lights, Power Grids And Essential Services Were Targeted?
A disruption to mobile networks could leave people unable to make calls or access the internet. But what happens when the systems affected are responsible for moving people around a city, supplying electricity to homes or ensuring that clean water reaches households?
Consider traffic lights. Modern traffic-management systems can connect signals, sensors and central control platforms to coordinate traffic flows. If a cyberattack disrupted such a system, the consequences could range from congestion and delays to dangerous conditions at busy intersections, depending on which controls were affected and what safeguards were in place.
The same principle applies to railway signalling, airport operations and other transport infrastructure. These systems do not all operate in the same way, and many have safety mechanisms designed to prevent failures from becoming accidents. But a disruption can still cause delays, force services to stop and affect thousands of people.
Electricity networks present another possibility. Power grids depend on digital systems to monitor equipment, manage distribution and help operators respond to changing demand. A cyberattack that interferes with these systems could force operators to isolate equipment or interrupt services while they investigate.
And electricity is not an isolated service. Supermarkets need it to operate their refrigeration systems. Telecom networks need power to keep equipment running. Hospitals rely on electricity for medical devices, lighting and essential operations, although backup generators and other safeguards can help maintain services during outages.
This creates a chain of dependencies. A disruption in one sector can create problems in another, even if the second sector was never directly targeted.
Water infrastructure raises similar questions. Treatment plants and distribution networks use monitoring and control systems to manage operations. If those systems were disrupted, operators might have to switch to manual procedures or temporarily interrupt parts of the service. The potential consequences would depend on the nature and duration of the disruption.
The larger concern is not that one cyberattack could automatically shut down an entire city. It is that several essential services depend on digital systems, and some of those services also depend on one another.
What if an attacker deliberately sought to exploit those connections? What if the objective were to create a series of relatively small disruptions that became more difficult to manage because they occurred at the same time?
That is the scenario worth considering.
Hospital Equipment Is Where The Consequences Could Become Serious
A supermarket that loses its refrigeration may have to discard thousands of euros worth of food. A transport network that experiences a technical disruption may face delays and congestion. But what happens when a cyberattack affects a hospital, where doctors and nurses depend on functioning equipment and timely access to patient information?
Hospitals are increasingly reliant on connected technology. Patient monitors, diagnostic machines, laboratory systems, digital records and equipment-management platforms all help medical staff deliver care. These systems can improve efficiency and allow information to move quickly between departments, but they also create dependencies that hospitals must manage.
Consider a hospital where a cyberattack makes patient records temporarily unavailable. Doctors may have difficulty accessing medical histories, medication details or test results. Staff might have to switch to paper records and manual procedures, slowing down work at a time when speed matters.
A disruption to diagnostic systems could delay scans or laboratory results. Problems with scheduling or hospital networks could affect appointments and the movement of patients between departments. Even when medical equipment continues to function, the loss of supporting digital systems can complicate treatment.
The concern becomes more acute when we consider connected medical devices. Equipment such as patient monitors and infusion pumps may rely on software, network connectivity or central monitoring systems, depending on the device and its configuration. A disruption could affect how information is displayed, transmitted or accessed.
This does not mean every connected medical device can be remotely controlled by an attacker. Medical equipment varies considerably, and hospitals use technical safeguards, clinical procedures and backup arrangements to manage failures. But those protections do not eliminate every risk associated with disruption to a connected healthcare environment.
These are hypothetical scenarios, but they illustrate why the consequences of cyberattacks cannot be measured only in financial losses or the number of computers affected.
The French supermarket incident raises a question about the physical consequences of digital interference. And that brings us to the wider issue running through all these examples: what happens when the systems connecting businesses, infrastructure and essential services become the very points through which disruption can spread?
Could One Cyberattack Disrupt An Entire Supply Chain?
The supermarket attack also raises a question that goes beyond individual devices and businesses. What happens when the same technology is used across an entire industry, connecting companies that depend on one another to keep goods and services moving?
Consider how food reaches a supermarket. It passes through producers, processing facilities, warehouses, refrigerated trucks and distribution centres before arriving on store shelves. Refrigeration is essential at several points along the way. If a major storage facility experiences a prolonged disruption, the consequences could extend to multiple retailers that depend on it for their supplies.
Now imagine that the problem is not a mechanical failure but a cyberattack affecting the systems used to manage that facility. The equipment might be physically intact, yet the business could struggle to maintain safe temperatures or operate normally. Deliveries could be delayed, goods might have to be discarded and retailers could face shortages.
The situation could become more complicated if several facilities relied on the same equipment manufacturer, software provider or remote-maintenance service. A vulnerability affecting a widely used system could potentially expose multiple businesses to similar problems.
This is one of the uncomfortable possibilities raised by the French incident. The point of vulnerability may not always be the supermarket itself. It could be a piece of technology used by hundreds of supermarkets, or a supplier that supports several parts of the same industry.
The same principle extends beyond food.
Manufacturers depend on suppliers for components, warehouses depend on inventory-management systems and delivery companies rely on software to coordinate vehicles and shipments. If an important part of that network becomes unavailable, the effects can spread to businesses that were never directly attacked.
A company assembling electronic equipment, for example, might have workers and machinery ready to operate but be unable to continue production because a critical component has not arrived. A warehouse might have goods in stock but struggle to process orders if its management system is unavailable. A pharmaceutical distributor might face difficulties if temperature-monitoring or inventory systems are disrupted.
The consequences could be particularly significant when businesses have limited alternatives. If a supplier is responsible for a specialised component or a central distribution facility serves a large area, replacing that capacity may not be straightforward.
Could attackers deliberately look for these dependencies? Could disrupting one relatively small but important component create a much larger problem for the businesses relying on it?
That is the broader scenario worth examining. A cyberattack does not necessarily have to affect every business in a supply chain. Interfering with one critical link could be enough to slow down the entire process.
And this is why the supermarket story matters beyond the immediate losses. It offers a way to think about the relationship between digital vulnerabilities and physical supply chains, where a problem that begins in one system can eventually affect the availability of goods and services elsewhere.
The Bigger Question About Our Connected World
The modern world runs on systems most people rarely think about.
That connectivity brings clear benefits. Businesses can manage equipment more efficiently, hospitals can share information faster and essential services can monitor operations across large networks. But it also means that the systems supporting everyday life are increasingly dependent on technology that can fail or be deliberately disrupted.
Extend that possibility to communications, transport, healthcare or energy, and the questions become much more serious.
The next major cyberattack may not be remembered only for the data it steals or the money it costs. It could be judged by what stops working in the physical world.
And that leaves us with one final question: in a world where so much depends on connected systems, how much disruption could begin with something as ordinary as a refrigerator?